The Tyranids are here!
Saturday, November 15, 2008


Thursday, November 13, 2008
Umi no Tririton 海のトリトン OP、ED
Used to love this song and I remembered I even watched this in Malay... Was a little sad near the end when his dolphin died, but its a great story for its time. And guess what? Same artist and 3 eye kid and Astroboy.
Wednesday, November 12, 2008
Factory Farming
Here is a video about factory farming which I urge you to watch, but not after a full meal. It contain some pretty cruel footage and that really makes me rethink about supporting the meal industry in this way. While, this video mentions about the Christian faith, I believe it should be a universal belief that we should not have the right to ill treat other living beings even if they eventually end up as food.
Monday, November 03, 2008
YSMenu Oct 2008
In case you are wondering what is this. We all know that R4 for NDS has stop developement for quite a while stuck at V1.18. Even the NDS code manager recently has been giving me problem updating the cheat list. There is a R4 SDHC and I am very sure just using the firmware is not going to make your R4 into a R4 SDHC. So, here is one of the shell I tried.
YSMenu is basically japanese and to make the firmware and files for the NDS requires a hell lot of steps. You can read all about it at :
http://www.gbatemp.net/index.php?showtopic=97615
but I had save you some time by prepaing it and patching it with the DSTT firmware from :
http://www.gbatemp.net/index.php?showtopic=71613
And to make it all right, I added the cheat list as of 28 Oct 2008. In addition, I even throw in the GBA/GBC Emulator into the package.
So, with all these works put in, tell me why you will not download this for a shot on your NDS R4?
Grab it at:
YSMenu Oct 2008
YSMenu is basically japanese and to make the firmware and files for the NDS requires a hell lot of steps. You can read all about it at :
http://www.gbatemp.net/index.php?showtopic=97615
but I had save you some time by prepaing it and patching it with the DSTT firmware from :
http://www.gbatemp.net/index.php?showtopic=71613
And to make it all right, I added the cheat list as of 28 Oct 2008. In addition, I even throw in the GBA/GBC Emulator into the package.
So, with all these works put in, tell me why you will not download this for a shot on your NDS R4?
Grab it at:
YSMenu Oct 2008
PSP Slim 5.00 M33-3
Yes, its time to do the 5.00 M33-3 update now. Its plain simple. Just unpack it to the root of your memory stick and patch and reboot. Tada, its now 5.00 M33-3.
BTW, you need 5.00 M33 in hte first place to perform this update.
Download 5.00 M33-3 here:
PSP 5.00 M33-3
BTW, you need 5.00 M33 in hte first place to perform this update.
Download 5.00 M33-3 here:
PSP 5.00 M33-3
PSP 5.00 M33 0xFFFFFFFF PSX Error Fix v2
This is the trickiest of the installation for 5.00 M33. Ok, make sure you are not connected using the USB connection menu. Exit that menu if you are. I have to presumed you had flashed 5.00 M33, because this file is patched on top of that firmware. What you need to do now is :
1. Press and hold [Select]
2. Change the USB Device to Flash 0
3. Exit
Now activate the USB connection menu. Go to this new weird drive. If you cannot see "KB" folder, make sure you unhide system and hidden directory in your Windows. Now, extract the package you download here to the root of this drive. Safe remove the drive and exit USB menu.
Repeat the above steps, but set it back to Memory Stick. You have just flashed a file into the firmware and this patch is done.
Download the PSX fix for 5.00 M33:
PSP 5.00 M33 PSX Fix
Basically, just for the fun of it. I heard that Popsloader still does not work properly and PSx seems to be a big problem in 5.x firmware. So, if you are a hardcode PSX gamer on PSP, I would suggest skipping the whole 5.00 M33 until I say its good for PSX. :)
Lastly, why this is v2, apparently, v1 doesn't work so well.
1. Press and hold [Select]
2. Change the USB Device to Flash 0
3. Exit
Now activate the USB connection menu. Go to this new weird drive. If you cannot see "KB" folder, make sure you unhide system and hidden directory in your Windows. Now, extract the package you download here to the root of this drive. Safe remove the drive and exit USB menu.
Repeat the above steps, but set it back to Memory Stick. You have just flashed a file into the firmware and this patch is done.
Download the PSX fix for 5.00 M33:
PSP 5.00 M33 PSX Fix
Basically, just for the fun of it. I heard that Popsloader still does not work properly and PSx seems to be a big problem in 5.x firmware. So, if you are a hardcode PSX gamer on PSP, I would suggest skipping the whole 5.00 M33 until I say its good for PSX. :)
Lastly, why this is v2, apparently, v1 doesn't work so well.
PSP Slim 5.00 M33 Savestate Plugin
Here is the usual savestate plugin for the PSP 5.00 M33 firmware. There is the readme.txt file in the root directory explaining how to use this plugin. The directory has been prepared for you. But before you go ahead and unpack it all to your root of the memory card, I would like to have your attention to the game.txt inside /seplugins. You will need to modify this file if you have other plugins. Basically, you need to include this line into your existing game.txt if you already had one. Otherwise, plain and simple, unpack them and enable it by holding your R button and do a cold reboot.
Download the PSP Slim 5.00 M33 Savestate plugin:
PSPS 5.00 M33 Savestate
P.S. I do not need to mention that this only works on firmware 5.00 M33, I hope.
Download the PSP Slim 5.00 M33 Savestate plugin:
PSPS 5.00 M33 Savestate
P.S. I do not need to mention that this only works on firmware 5.00 M33, I hope.
PSP Slim 5.00 M33
If you follow my blog, you should know my updates are usually very slow. The reason is I usually prefer to only post updates which I am confident and tested. So, here is the 5.00 M33 release for so long. There is 3 parts to this update. It consist of the core 5.00 M33 firmware, 1 bug fix for playing PSX game having 0xFFFFFFFF error and the usual savestate plugin for 5.00 M33. Nevertheless the 2 are optional and if you do not use them, you can do without. Therefore, I had post them separately.
Here is the Core firmware. The usual applies. Unpack it to the root of your memory card as all the directories has been created for you. DO NOT FORGET TO PRESS O TO REBOOT AT THE END OF THE FLASHING!!! Or you will brick you PSP as usual.
Download PSP 5.00 M33:
PSP 5.00 M33
Here is the Core firmware. The usual applies. Unpack it to the root of your memory card as all the directories has been created for you. DO NOT FORGET TO PRESS O TO REBOOT AT THE END OF THE FLASHING!!! Or you will brick you PSP as usual.
Download PSP 5.00 M33:
PSP 5.00 M33
Sunday, October 26, 2008
Hack in the Box 2008
After 1 year of lapse, I will be going again. Well, not presenting this time too. should had prepared well if I wanted to. anyway, it will be a whole week burned there. I miss some of the best things there like good food at Ka So etc. This time its held at a different location and things are very different.
For full details on what will be presented, check out the HITB website at :
http://conference.hitb.org/hitbsecconf2008kl/agenda.htm
Its pretty obvious I will be stuck in Track 2 because the first one from Track 1 is from Oracle. Of course, other reasons are the speakers from Track 2 are my usual favorites.
Anyway, if you are there at HITB, I hope I can meet you there for a chat. See ya there!
For full details on what will be presented, check out the HITB website at :
http://conference.hitb.org/hitbsecconf2008kl/agenda.htm
Its pretty obvious I will be stuck in Track 2 because the first one from Track 1 is from Oracle. Of course, other reasons are the speakers from Track 2 are my usual favorites.
Anyway, if you are there at HITB, I hope I can meet you there for a chat. See ya there!
Microsoft Windows RPC Vulnerability KB9358644 MS08-067 (CVE-2008-4250)
I seldom have to nag about a Windows Update. This one is an exception. The reason being that it affects a large amount of machine and many of which are still the popular choices around like Windows XP and 2003. The outbreak, if it happens, can easily match that of the Slammers or Code Red. This is the only reason why I STRONGLY urge everyone reading this to make sure this update is put in.
Another reaon is probably not a good news. The bad guys beats us to it again as usual. There had been signs of attacks based on this exploits in the past 2 weeks and in fact now, there are 2 known trojans (info collector so far) which made use of this exploit. This exploit is serious enough for Microsoft to issue a special bulletin in their security software which reminds the user to update their machines in order to avoid infection.
So, can you please do this upgrade if you have not on 24 Oct 2008. You can download the files directly or use the normal Windows update to get this patch.
For a more detail FAQ :
http://blogs.securiteam.com/index.php/archives/1150
Another reaon is probably not a good news. The bad guys beats us to it again as usual. There had been signs of attacks based on this exploits in the past 2 weeks and in fact now, there are 2 known trojans (info collector so far) which made use of this exploit. This exploit is serious enough for Microsoft to issue a special bulletin in their security software which reminds the user to update their machines in order to avoid infection.
So, can you please do this upgrade if you have not on 24 Oct 2008. You can download the files directly or use the normal Windows update to get this patch.
For a more detail FAQ :
http://blogs.securiteam.com/index.php/archives/1150
Sunday, October 19, 2008
科學小飛俠 ~ 日文版
And here I present you the original version in Japanese with enhanced graphics comparing the 80s and the 90s version.
科學小飛俠 ~ 台灣版
This is a very very rare OP version of the anime Battle of the Planets / Gatchaman / Science Ninja Team. This is the Taiwanese dubbed edition.
Tuesday, October 14, 2008
Russian Company manages to break WPA/WPA2 100 with GPU
Using GPU to help in a distributed attack on the WPA / WPA2 keys, days or at most weeks is all it take to break the WPA key now...
Is this the beginning of the end? Even when 802.11n is still in draft, WPA2 is dead?
Read all about it :
http://securityandthe.net/2008/10/12/russian-researchers-achieve-100-fold-increase-in-wpa2-cracking-speed/
Is this the beginning of the end? Even when 802.11n is still in draft, WPA2 is dead?
Read all about it :
http://securityandthe.net/2008/10/12/russian-researchers-achieve-100-fold-increase-in-wpa2-cracking-speed/
風暴 - TVB 少年四大名捕主題曲 完整版 ~ 林峯 吳卓羲 馬國明 陳鍵鋒

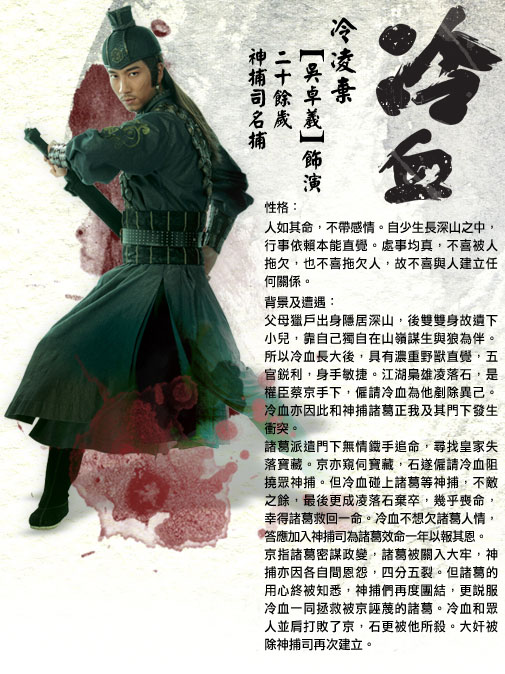
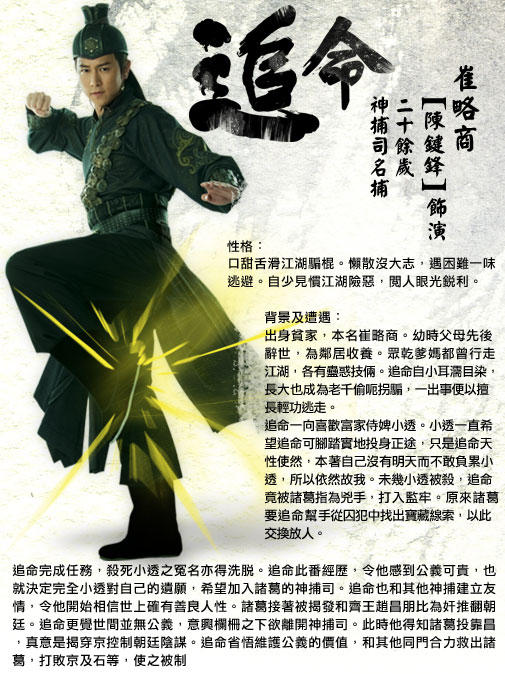
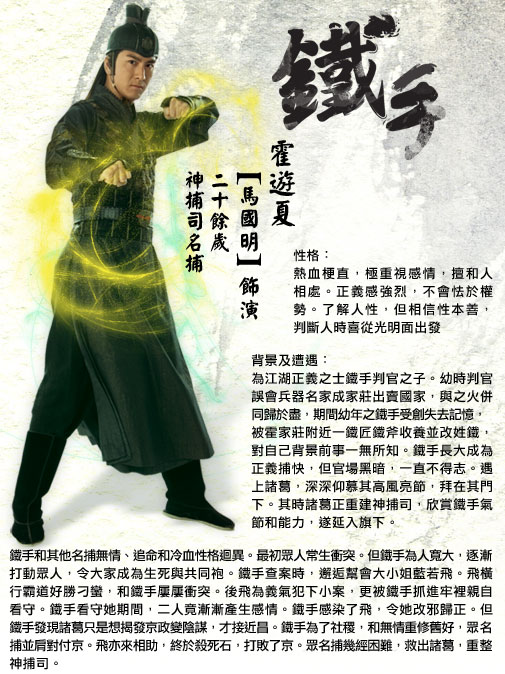

風暴 - TVB 少年四大名捕主題曲 完整版 ~ 林峯 吳卓羲 馬國明 陳鍵鋒
曲:鄧智偉、葉肇中 詞:鄭櫻綸
林 峰:
如若你不再逗留
我為了夢想的守候
曾為你心碎過後 長痛承受
吳卓羲:
如若你走盡頭 痛恨似在一生左右
如學會放低所有
無悔今後
馬國明:
風雨中 背叛裏似失控
當日我怎付出 才像惡夢
陳鍵鋒:
飄泊中 背負了有多重
情褪去才看懂
合 唱:
才相信
為何尋覓總可感到 渺無尺度
為何沉默只可能得到 烈變風暴
誰人曾被風急輕掃 也留記號
誰人來用心的擺佈
烈變風暴 再度
林 峰:
平靜各走各路途
蘊釀那未知的風暴
吳卓羲:
難避過創傷苦惱 悉緒的霧
馬國明:
風雨中 背叛裏似失控
當日我怎付出 才像惡夢
陳鍵鋒:
飄泊中 背負了有多重
情褪去才看懂
合 唱:
才相信
為何尋覓總可感到 渺無尺度
為何沉默只可能得到 烈變風暴
誰人曾被風急輕掃 也留記號
誰人來用心的擺佈
烈變風暴 再度
誰人曾被風急輕掃 也留記號
誰人來用心的擺佈
烈變風暴 再度
Tuesday, October 07, 2008
Slayers Revolution
After many many years of waiting, Slayers is finally back! Yes, and Season 4 named Slayers Revolution is completed as at episode 13! Here is the OP and the ED for your viewing pleasure!
And yes, the next season will be Slayers Glory!
And yes, the next season will be Slayers Glory!
Monday, October 06, 2008
Tuesday, September 30, 2008
Who killed Server Rabbit? Finale
The root of the cause was right there. How could I had missed it? Both the servers were hardened and rebooted on different dates due to the Windows Update. I got hold of the details of the hardening and released that due to the inheritance properties, the hardening of the permission in hte registry has been perform on the "service" branch instead of the individual services. Several critical roles such as "Power Users" were actually removed as part of the hardening processes.
Now, take a step back. So what? I still ahve admin running and it was not working when I log in as admin. The reason being even if you are admin, it does not mean all the services are run as admin. Some of them are still run as other roles and these role unfortunate to say happens to be one of the removed one!
My gut feeling this was the root cause. I checked with another working server / workstation and restored the deleted roles into one of the Server Rabbit and ta-da... Everything was working and kicking again. Actually as long as RPC service is up, I pretty much knew I hit it.
Well, here is the aftermath of the whole incident.
1. There are malware found. Incidentally, this means the malware protection is not enough. Even if this time the malware did not take it down, sometimes in the future, it will.
2. There was no backup. Having a good snapshot / backup will save the situation and minimize the downtime required to recover the whole problem.
3. There is not enough documentation. This applies to logging as well. If there logs and documents are properly put in place, the whole incident could had been easily tracked simply from the look of the documentations.
4. There is insufficent training. While its a good idea to have some of the admin learn how to harden or improve certain functions, it is always good to provide the admin sufficent training to do so. With proper training / certification, the admin would had avoided the incident.
5. Access control was not properly inplemented. The sharing of accounts had made the whole investigation a nightmare. If individual accounts were used, combined with properly logging, it would had provided the information who made some change at what time. This could had greatly help the investigation.
6. Logging is the last time that I felt was missing. In terms of the firewall, IDS etc. If proper logs were generated, I would had concluded whether this was a security incident or not from the very start based on who has accessed the server etc. Of course lets not forget the golden rule that if a machine is compromized, the log is as good as none. Therefore logs from hardware boxes (which is probably not the target of the attack) is greatly helpful in determining whether a real intrusion has taken place or was it simply a misconfigureation or software corruption.
I am glad this was not my day in day out job. :) Well if it is, I am hell not getting paid enough for this. :)
Now, take a step back. So what? I still ahve admin running and it was not working when I log in as admin. The reason being even if you are admin, it does not mean all the services are run as admin. Some of them are still run as other roles and these role unfortunate to say happens to be one of the removed one!
My gut feeling this was the root cause. I checked with another working server / workstation and restored the deleted roles into one of the Server Rabbit and ta-da... Everything was working and kicking again. Actually as long as RPC service is up, I pretty much knew I hit it.
Well, here is the aftermath of the whole incident.
1. There are malware found. Incidentally, this means the malware protection is not enough. Even if this time the malware did not take it down, sometimes in the future, it will.
2. There was no backup. Having a good snapshot / backup will save the situation and minimize the downtime required to recover the whole problem.
3. There is not enough documentation. This applies to logging as well. If there logs and documents are properly put in place, the whole incident could had been easily tracked simply from the look of the documentations.
4. There is insufficent training. While its a good idea to have some of the admin learn how to harden or improve certain functions, it is always good to provide the admin sufficent training to do so. With proper training / certification, the admin would had avoided the incident.
5. Access control was not properly inplemented. The sharing of accounts had made the whole investigation a nightmare. If individual accounts were used, combined with properly logging, it would had provided the information who made some change at what time. This could had greatly help the investigation.
6. Logging is the last time that I felt was missing. In terms of the firewall, IDS etc. If proper logs were generated, I would had concluded whether this was a security incident or not from the very start based on who has accessed the server etc. Of course lets not forget the golden rule that if a machine is compromized, the log is as good as none. Therefore logs from hardware boxes (which is probably not the target of the attack) is greatly helpful in determining whether a real intrusion has taken place or was it simply a misconfigureation or software corruption.
I am glad this was not my day in day out job. :) Well if it is, I am hell not getting paid enough for this. :)
Thursday, September 25, 2008
Samsung Omnia / Orca Firmware HH3
Its out! Finally. While a HI3 is already leaked, the official ROM is not at HH3.
What are you waiting for? Grab it at :
http://www.samsungmobile.com/promotion/omnia/sg/sub02_Vista.jsp
What are you waiting for? Grab it at :
http://www.samsungmobile.com/promotion/omnia/sg/sub02_Vista.jsp
CWCheat 0.22D
Its been a while since I updated this. Anyway, same drill. The latest (as of 25 Sep 2008) GameDB is loaded in. This is a package for the PSP Slim. Just unpack all to the root directory of your memory card of your PSP. Take note of the few *.txt file. If you have other plugins, you may want to manually edit them in instead of replacing it. Especially GAME.TXT, if you are a big fan of mine, then you will probably have the USB Charge and the Save state of the 4.01 FW.
Here is the download :
http://rapidshare.com/files/148169481/CWCheat22D.zip
Here is the download :
http://rapidshare.com/files/148169481/CWCheat22D.zip
Subscribe to:
Posts (Atom)